


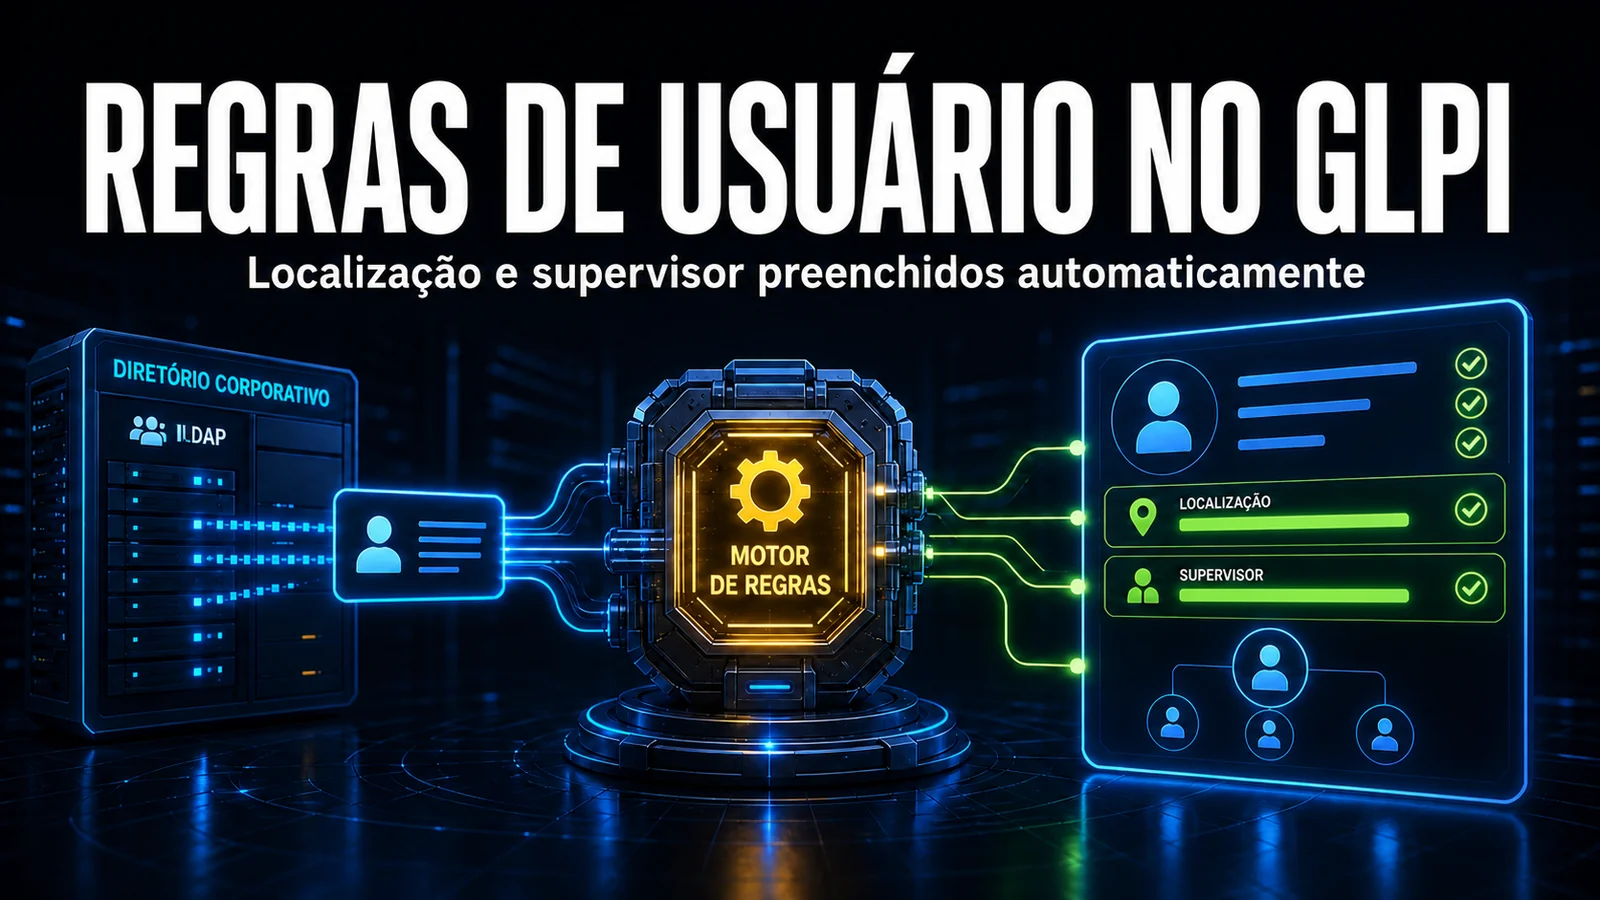
The criterion exists, the action does not. GLPI rights rules read AD group, organisational unit and e-mail domain effortlessly — but when it comes to writing that data onto the user record, the engine simply offers no option.
The problem
Anyone integrating GLPI with Active Directory knows the scene: the user rights assignment rule recognises perfectly that John sits in the "São Paulo Branch" OU and the "Finance" group. That is enough to assign a profile and an entity. But Location, Supervisor, Category and Title stay empty — and somebody fills them in by hand, user by user.
The outcome is predictable: fields nobody maintains become fields nobody trusts. Reports by location are wrong, escalation by supervisor does not work, and the user base ages badly.
The usual workarounds are poor: patch the GLPI core (and inherit the problem on every upgrade) or keep an external sync routine that nobody documents.
How Rule Extender works
The module adds new actions to RuleRight, the rights rule engine GLPI already ships. The criteria remain the native ones; what changes is what the rule can do once they match.
- Assign Location — derive it from the group, the OU or the e-mail domain.
- Assign Supervisor — the responsible person is set by rule, not by typing.
- Assign user Category and Title — consistent classification from the first login.
- No custom table, no patch — the module extends the existing engine; nothing in the core is edited.
How to enable it
- Install NexTool on your GLPI 11.
- Go to NexTool > Modules and enable Rule Extender.
- Open Administration > Rules > Rights assignment rules.
- Create or edit a rule: criteria stay native and the new actions appear in the list.
Who it is for
Environments authenticating through LDAP or Active Directory with enough users that filling records by hand stops being viable — usually from a few dozen upwards. It is also the groundwork for anyone who wants supervisor-based escalation or location reports and found the fields empty.
Compatibility
- GLPI: 11.0+
- Plan: Licensed
- Plugin: NexTool 6.x+
Next step
Rule Extender is part of NexTool, an ecosystem of modules that extends GLPI without code customisation. Visit the module page or book a call to see it running in your environment.
Reviewed by the NexTool Solutions team.



